Charities warned to up their game on cyber security for donors
Charities in Yorkshire need to seriously up their game on cyber security to avoid customer data being hacked by criminals.
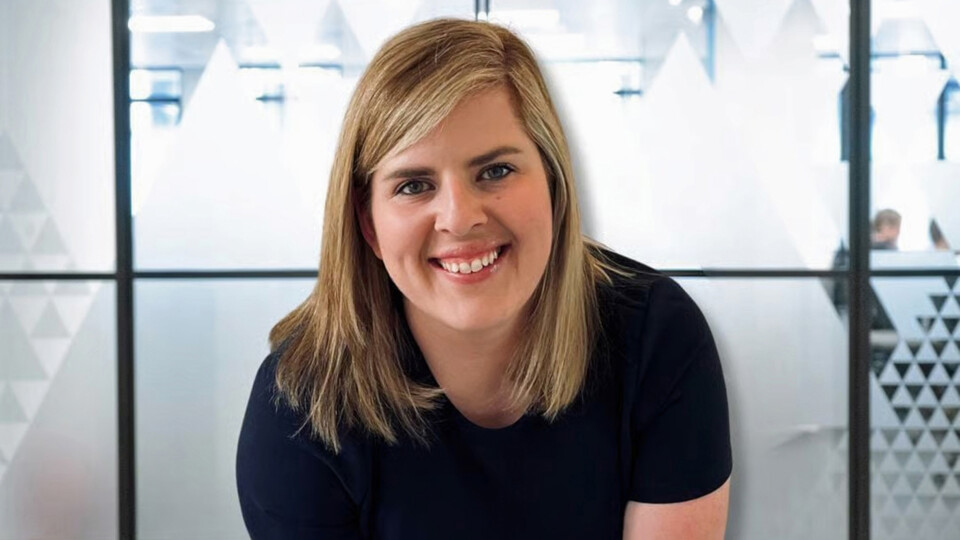
That is the call to action from Siobhan Holmes, a specialist in not-for-profit organisations such as charities.
“Encryption alone is not enough – strong identity, access management and robust policies are equally vital,” she warned.
Siobhan is a partner at UK top 10 accountancy and business advisory firm Azets, which has offices in Leeds, Bradford and York.
She provided the stark reminder after a customer relationship management (CRM) platform used by more than 1,000 charities through a single technology provider was breached.
Siobhan said: “The hack highlights just how dependent the fundraising sector has become on shared technology providers.
“For hackers, many charities have an ‘Achilles’ heel’ when it comes to IT, shooting their virtual arrows through thin firewalls to wreak havoc.
“Charities do need to significantly strengthen their cyber security to avoid customer data being stolen and used to commit financial fraud such as taking out credit cards or loans in the names of donors.
“Let’s be clear – registered charities in the UK in 24/25 had a total income of £102 billion, with millions of customers on databases, so the sector represents a soft target with the prospect of rich customer data pickings; the reputational damage this could cause is immeasurable.
“Micro and small charities make up around 75% of the charity sector, with incomes of less than £10,000 and up to £100,000 respectively.
“The risk of being in the crosshairs of cyber thieves is therefore even higher because many charities simply cannot afford to make their CRMs as impregnable as they can be.”
Charities use a CRM portal, either in-house or through a technology provider, to collect donations online, sell event tickets, manage memberships and email updates to customers.
Siobhan added: “For trustees, executives and finance leaders, the major CRM breach must prompt an important question which is not just ‘how secure are we?’ but ‘how secure are the suppliers and platforms we rely on?’”
“With cyber attacks continuing to affect organisations across the sector, cyber resilience must be viewed as a fundamental part of governance, risk management and safeguarding public trust.
“Protecting beneficiaries, donors and sensitive data is no longer solely the responsibility of IT teams – it’s the responsibility of people in charge of the charity which includes the trustees who perhaps are out of their depth when it comes to IT.
“Cyber security should not only be a key item on the risk register, but it should also be a standing item for Board meetings to ensure strong governance and challenge by the trustees.”
One of the lessons from the breach was that a single compromised AWS access key was enough to enable the attack, “demonstrating the critical importance of credential management and access controls”.
An AWS access key is a security credential to verify who you are and whether you have permission to get under the bonnet of the computer programme.
Siobhan said: “Although the data was encrypted at rest, the attacker used valid credentials to access and download information in a readable form.
“Encryption alone is not enough. Strong identity and access management are equally vital.
“If major corporate brands such as Jaguar Land Rover and M&S can be hit, so can charities.
“Charities with CRMs need to urgently review cyber security and seek professional advice – it is not something that can be scrimped on.”
There are nearly 171,400-plus registered charities in UK, according to latest sector figures, with 1.7m employees, 6.5m volunteers and more than 921,000 trustees.
Earlier this year Siobhan urged charities and not-for-profit organisations to ensure their procedures and records are watertight in light of new and intensified compliance activity by HMRC.